Sébastien Rigaux

Tech watch

← All links

Dependency management

Tracking, updating and controlling libraries and tools used by a project.

NewReleases logo: “new” in blue and “(releases)” in black on a white background.

NewReleases tracks new project and package versions across platforms such as GitHub, npm, NuGet, and Docker Hub, then sends alerts by email, instant messaging, or webhook. It removes the need to check each dependency or tool manually.

Notifications can be instant or scheduled, and tracking can be configured from dependency files such as package.json, requirements.txt, or go.mod. Regular-expression and prerelease-status filters help narrow down which versions trigger alerts.

Janoš Guljaš

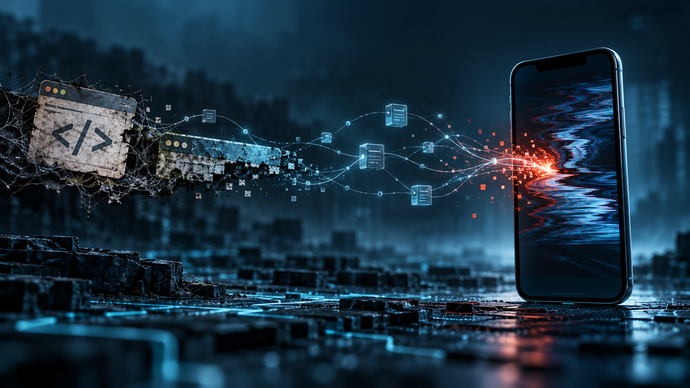
An illustration shows a dilapidated web code tag connected by digital streams to an iPhone struck by a red and blue distortion.

Expired domains behind old analytics and advertising tags have been bought and repurposed to redirect visitors to malicious content, including the Coruna and DarkSword iOS exploit kits. Report URI and iVerify describe a chain that filters visitors and tailors its payload to the device; security scanners may receive only an empty response.

The case shows how a forgotten third-party script remains an active dependency: its domain can change hands without any site change. The article recommends auditing tags, monitoring loaded scripts, and restricting their domains with a Content Security Policy.

Scott Helme

Header illustration for the React folder structure article on Robin Wieruch’s site

This comprehensive overview walks through organizing a React project, from a single file to a modular monorepo structure. The author details how to split code (files, technical folders, feature folders, domains, packages) and the impact of each approach on maintainability, dependency isolation, and scalability. Concrete examples illustrate how to evolve the architecture as the project grows, with clear rules to prevent cross-feature dependencies and encourage reuse.

Robin Wieruch